Evaluate the enterprise reference
ScaleEnterprise Agentic AI Platform Blueprint
Multi-account AWS CDK reference blueprint for an enterprise Agent Factory with AWS Organizations, SCPs, CDK Pipelines, evaluation gates and a documented support envelope.
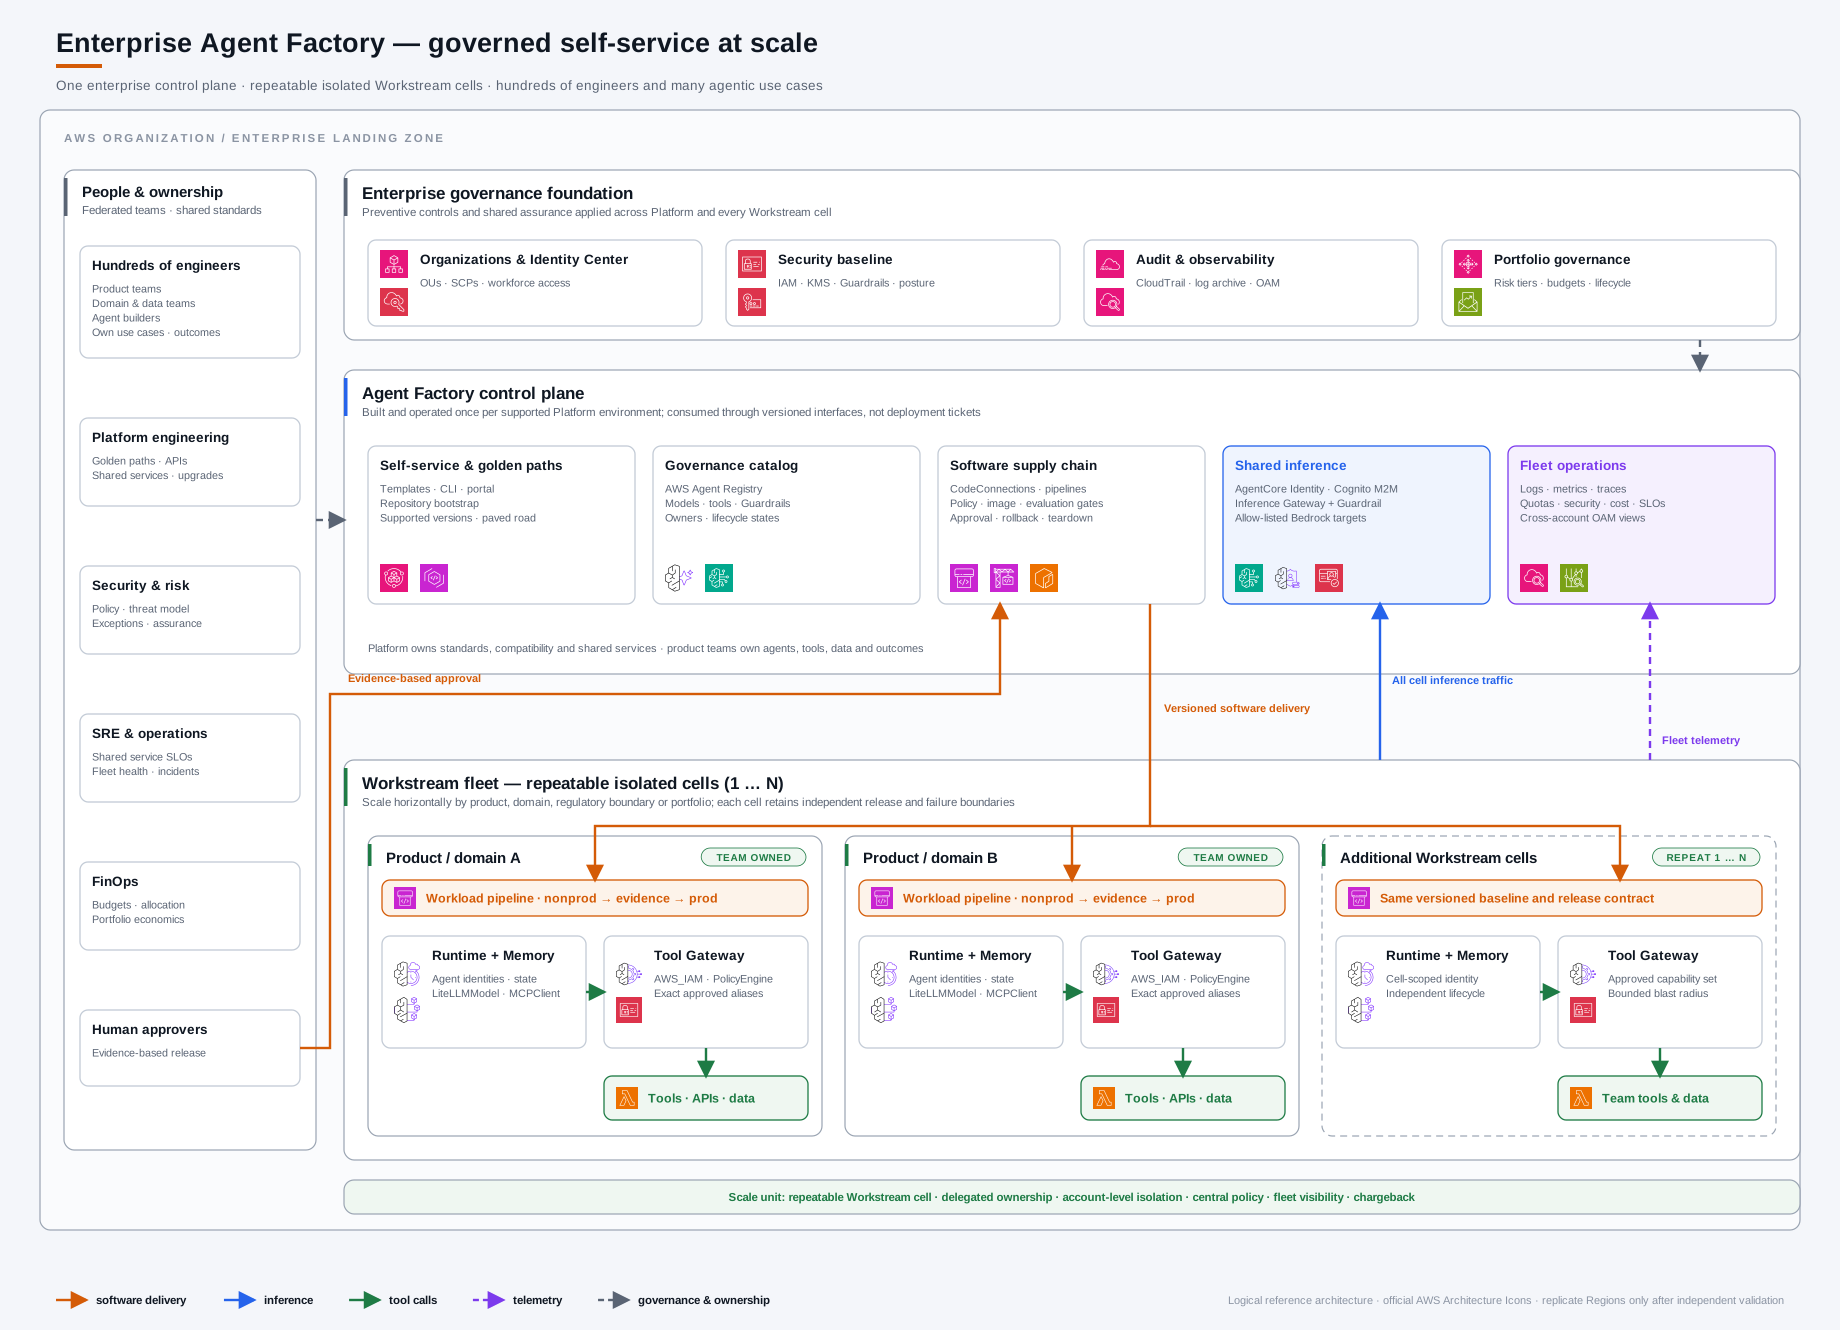
What it is
- Multi-account architecture with Management, Platform, and Workstream account roles Source: README.md: 2.1 Logical topology and cardinality (opens in new tab)
- Service control policies for model, Region, Guardrail, Registry, Gateway, and deployment boundaries Source: README.md: 10.1 Control summary (opens in new tab)
- Per-tenant Application Inference Profiles Source: agentic-app.ts (opens in new tab), README.md: 4. AWS services used (opens in new tab)
- Private VPC with interface endpoints (no NAT) Source: agentic-vpc-construct.ts (opens in new tab), README.md: 4. AWS services used (opens in new tab)
- Evaluation gate in the Runtime/Memory pipeline shape Source: README.md: 6.5 Onboard a Workstream cell (opens in new tab)
- Fleet observability with CloudWatch OAM Source: README.md: 10.1 Control summary (opens in new tab)
- Adversarial evidence model: every negative test needs an authorized positive twin Source: README.md: 10.2 Threat and evidence model (opens in new tab)
Status
- Version
- 1.0.0 README.md (opens in new tab)
- Status
- Version 1.0.0 (README badge); two open advisories (issues #29 and #30) README.md (opens in new tab)
Advisory: GitHub issue #29
Opened 2026-09-15. The blueprint still provisions and consumes Agent Registry through the preview bedrock-agentcore-control APIs, and AWS support for those APIs ended on 2026-09-17. Treat Registry-dependent paths as unverified until the issue is closed.
enterprise blueprint: migrate Agent Registry before 2026-09-17 preview cutoff (opens in new tab)
Advisory: GitHub issue #30
Opened 2026-09-15. The lockfile resolves aws-cdk-lib to 2.251.0; advisory GHSA-vcrf-j523-4mrf (CVE-2026-13760, high) is fixed in aws-cdk-lib 2.260.0. This is a build and deployment toolchain risk; run npm audit and update before deploying.
enterprise blueprint: resolve npm audit findings before deployment (opens in new tab)
Evidence: package-lock.json (opens in new tab)
At a glance
| Fact | Value | Source |
|---|---|---|
| Validated regions | Validated in eu-west-1; SCP allow-list us-west-2, us-east-1, eu-west-1 The SCP region allow-list comes from PLATFORM_APPROVED_REGIONS in packages/platform-baselines/src/approved-regions.ts. A different Region is a new validation target, not a configuration-only substitution. | README.md: 5. Prerequisites (opens in new tab) |
| Default region | eu-west-1 | README.md: 6.1 One-time setup (opens in new tab) |
| What it deploys | A multi-account reference: AgentCore Runtime, Gateway, Identity, Memory, Policy, Registry and Evaluations; Bedrock with Guardrails and application inference profiles; Cognito, IAM Identity Center and Cedar; Organizations SCPs; CodePipeline, CodeBuild and CodeConnections; VPC with endpoints; Lambda; KMS, S3, DynamoDB, Secrets Manager and ECR; CloudWatch, OAM and X-Ray; CloudTrail, Config, Security Hub, GuardDuty and Inspector; Budgets and CUR README section 4 calls this the deployable and live-tested reference implementation, not a universal mandatory product list. Not every optional construct is inside the Ireland support envelope. | README.md: 4. AWS services used (opens in new tab) |
| First deploy | not documented The README documents the deployment sequence (sections 6.1 to 6.6: one-time setup, configuration, scoped bootstrap, Platform pipeline, Workstream onboarding, validation) but no duration. | none |
| Hands-on time | not documented The README lists organizational prerequisites (a Platform product owner, an account-vending process, governance and approval policies) but gives no time figure. | none |
| Cost | not documented README section 8 describes a two-layer cost model (shared Platform cost and Workstream cost) and recommended controls such as allocation tags, budgets and CUR reconciliation, but publishes no figure. | none |
| Infrastructure as code | AWS CDK (TypeScript) with CDK Pipelines; 12 service control policies; Python and shell utilities | README.md (opens in new tab) |
| Account topology | Multi-account: Management, Platform, and Workstream account roles (nonproduction and production may be separate accounts) | README.md: 5. Prerequisites (opens in new tab) |
| Auth and policy | AWS_IAM on the Workstream Tool Gateway; Cognito M2M and AgentCore Identity for inference; AgentCore PolicyEngine plus a retained Lambda Cedar wrapper; 12 SCPs | README.md: 10.1 Control summary (opens in new tab) |
| Status | Version 1.0.0 (README badge); two open advisories (issues #29 and #30) | README.md (opens in new tab) |
| Teardown | Run python3 scripts/final_teardown.py per account role (workstream, then platform, then management), first as a dry run and then with --apply; verify with scripts/residue_inventory.py | README.md: 16. Cleanup (opens in new tab) |
| Version | 1.0.0 | README.md (opens in new tab) |
Quickstart
Prerequisites and deployment sequence
Prerequisites: Blueprint prerequisites on the Start pages.
The Blueprint is a multi-account rollout, not a single command. Start with one representative Workstream cell and prove the complete lifecycle before onboarding more.
Expected time: not documented The README documents the deployment sequence (sections 6.1 to 6.6: one-time setup, configuration, scoped bootstrap, Platform pipeline, Workstream onboarding, validation) but no duration.
Confirm the prerequisites (README section 5)
Node.js 20 or later, Python 3.12 or later, AWS CLI v2 and AWS CDK v2. An AWS Organizations landing zone with Management, Platform and Workstream account roles. A GitHub organization with an AWS CodeConnections connection. Bedrock model access in the target Region. Administrator access for the initial bootstrap only.
6.1 One-time setup
git clone https://github.com/aws-samples/sample-ai-agent-factory.git
cd sample-ai-agent-factory/enterprise-agentic-ai-platform-blueprint
npm ci
npm run build
npm test
npm run lint
npm run scrub

export AWS_REGION=eu-west-1
export AWS_DEFAULT_REGION="$AWS_REGION"
export CDK_DEFAULT_REGION="$AWS_REGION"
Set all three Region variables; setting only CDK_DEFAULT_REGION is insufficient.
6.2 Configuration
The CDK application reads agenticai/* context values. Keep real account IDs, secret ARNs, tokens and generated Registry context outside source control, and pin agenticai/githubBranch when deploying an unmerged branch.
6.3 Bootstrap with scoped policies
Generate one CloudFormation execution policy per account and Region, validate each with IAM Access Analyzer, then run the cross-account bootstrap. Do not use AdministratorAccess as the execution policy.
README section 6.3, Bootstrap with scoped policies (opens in new tab)
Source: README.md: 6.3 Bootstrap with scoped policies (opens in new tab)
6.4 Deploy the Platform control plane
Create the Platform pipeline stack with Gateway invoke permissions disabled, run it, and review Registry descriptors before approval.
README section 6.4, Deploy the Platform control plane (opens in new tab)
Source: README.md: 6.4 Deploy the Platform control plane (opens in new tab)
6.5 Onboard a Workstream cell
Resolve one Registry context file per environment, deploy the Workload pipeline root, complete the two-phase Gateway permission handoff, then approve GatewayPermissionReady.
README section 6.5, Onboard a Workstream cell (opens in new tab)
Source: README.md: 6.5 Onboard a Workstream cell (opens in new tab)
6.6 Validation
Run the local gates, synthesize with strict mode, and require clean cdk-nag reports. Live mode fails closed: missing credentials or expected denials are errors, not skips.
Service control policies
The Blueprint ships 12 service control policies as TypeScript definitions. Each entry links to its source file.
SCP-01Restrict Bedrock Model Access: scp-01-model-allowlist.ts (opens in new tab)SCP-02Enforce Bedrock Guardrail Usage: scp-02-enforce-guardrail.ts (opens in new tab)SCP-03Enforce VPC Endpoints for AgentCore: scp-03-enforce-agentcore-vpce.ts (opens in new tab)SCP-04Enforce VPC Endpoints for Bedrock: scp-04-enforce-bedrock-vpce.ts (opens in new tab)SCP-05Deny Guardrail Modification in Workload Accounts: scp-05-deny-guardrail-modification.ts (opens in new tab)SCP-06Restrict Region Usage: scp-06-restrict-regions.ts (opens in new tab)SCP-07Deny Public AgentCore Resources: scp-07-deny-public-agentcore.ts (opens in new tab)SCP-08Deny ECR Public Repositories: scp-08-deny-ecr-public.ts (opens in new tab)SCP-09AgentCore Gateway Mutation Lockdown: scp-09-gateway-mutation-lockdown.ts (opens in new tab)SCP-10Tool-Invoke Allow-list: scp-10-tool-invoke-allowlist.ts (opens in new tab)SCP-11Agent Registry Mutation Lockdown: scp-11-registry-mutation-lockdown.ts (opens in new tab)SCP-12Developer Permission Set and Platform-Tag Mutation Deny: scp-12-developer-platform-tag-deny.ts (opens in new tab)
Golden paths
The blueprints under blueprints/ are starting points for versioned enterprise golden paths, not disconnected demos. README.md: 7. Golden paths for engineering teams (opens in new tab)
| Template | Framework | Best fit | Enterprise contract |
|---|---|---|---|
agenticai-task-agent (opens in new tab) | Strands | Deterministic business task | Max-iteration guard, baseline Guardrail, optional durable HITL |
agenticai-chatbot-agent (opens in new tab) | Strands | Customer or employee conversation | Streaming, conversation memory, human handoff |
agenticai-multi-agent (opens in new tab) | Strands | Supervisor and bounded workers | Separate identities, explicit delegation, bounded fan-out |
agenticai-langgraph-agent (opens in new tab) | LangGraph | State-machine or graph orchestration | Same Gateway and governance boundaries through an adapter |
agenticai-crewai-agent (opens in new tab) | CrewAI | Role-oriented crew orchestration | Same approved-tool and Guardrail contracts through an adapter |
Source: README.md: 7. Golden paths for engineering teams (opens in new tab)
Repository map
The packages/ folder holds 35 packages. The groups below are a reading aid; the names are as in the repository. Browse packages/ on GitHub (opens in new tab)
Organization, accounts and access
landing-zoneorganizationsplatform-baselinesdeveloper-accessfederationcost-allocation
AgentCore and application constructs
agentcore-gatewayagentcore-identityagentcore-memoryagentcore-registryagentcore-runtimeagent-registryagentic-appagentic-vpc
Model access, quotas and safety
platform-inference-gatewaylitellm-gatewaybedrock-guardrailsbedrock-invocation-loggingbedrock-quotastenant-quota-guardpii-redaction
Tools, catalogue and policy
platform-tool-cataloguetool-cedar-wrappercatalogue-drift-detectoragent-protocolsrag
Delivery, evaluation and lifecycle
agent-lifecycleagent-resilienceevaluation-gatesonline-evaluationhitldeveloper-cli
Observability and compliance
observabilityotel-genai-semconveu-ai-act-compliance
Architecture and figures
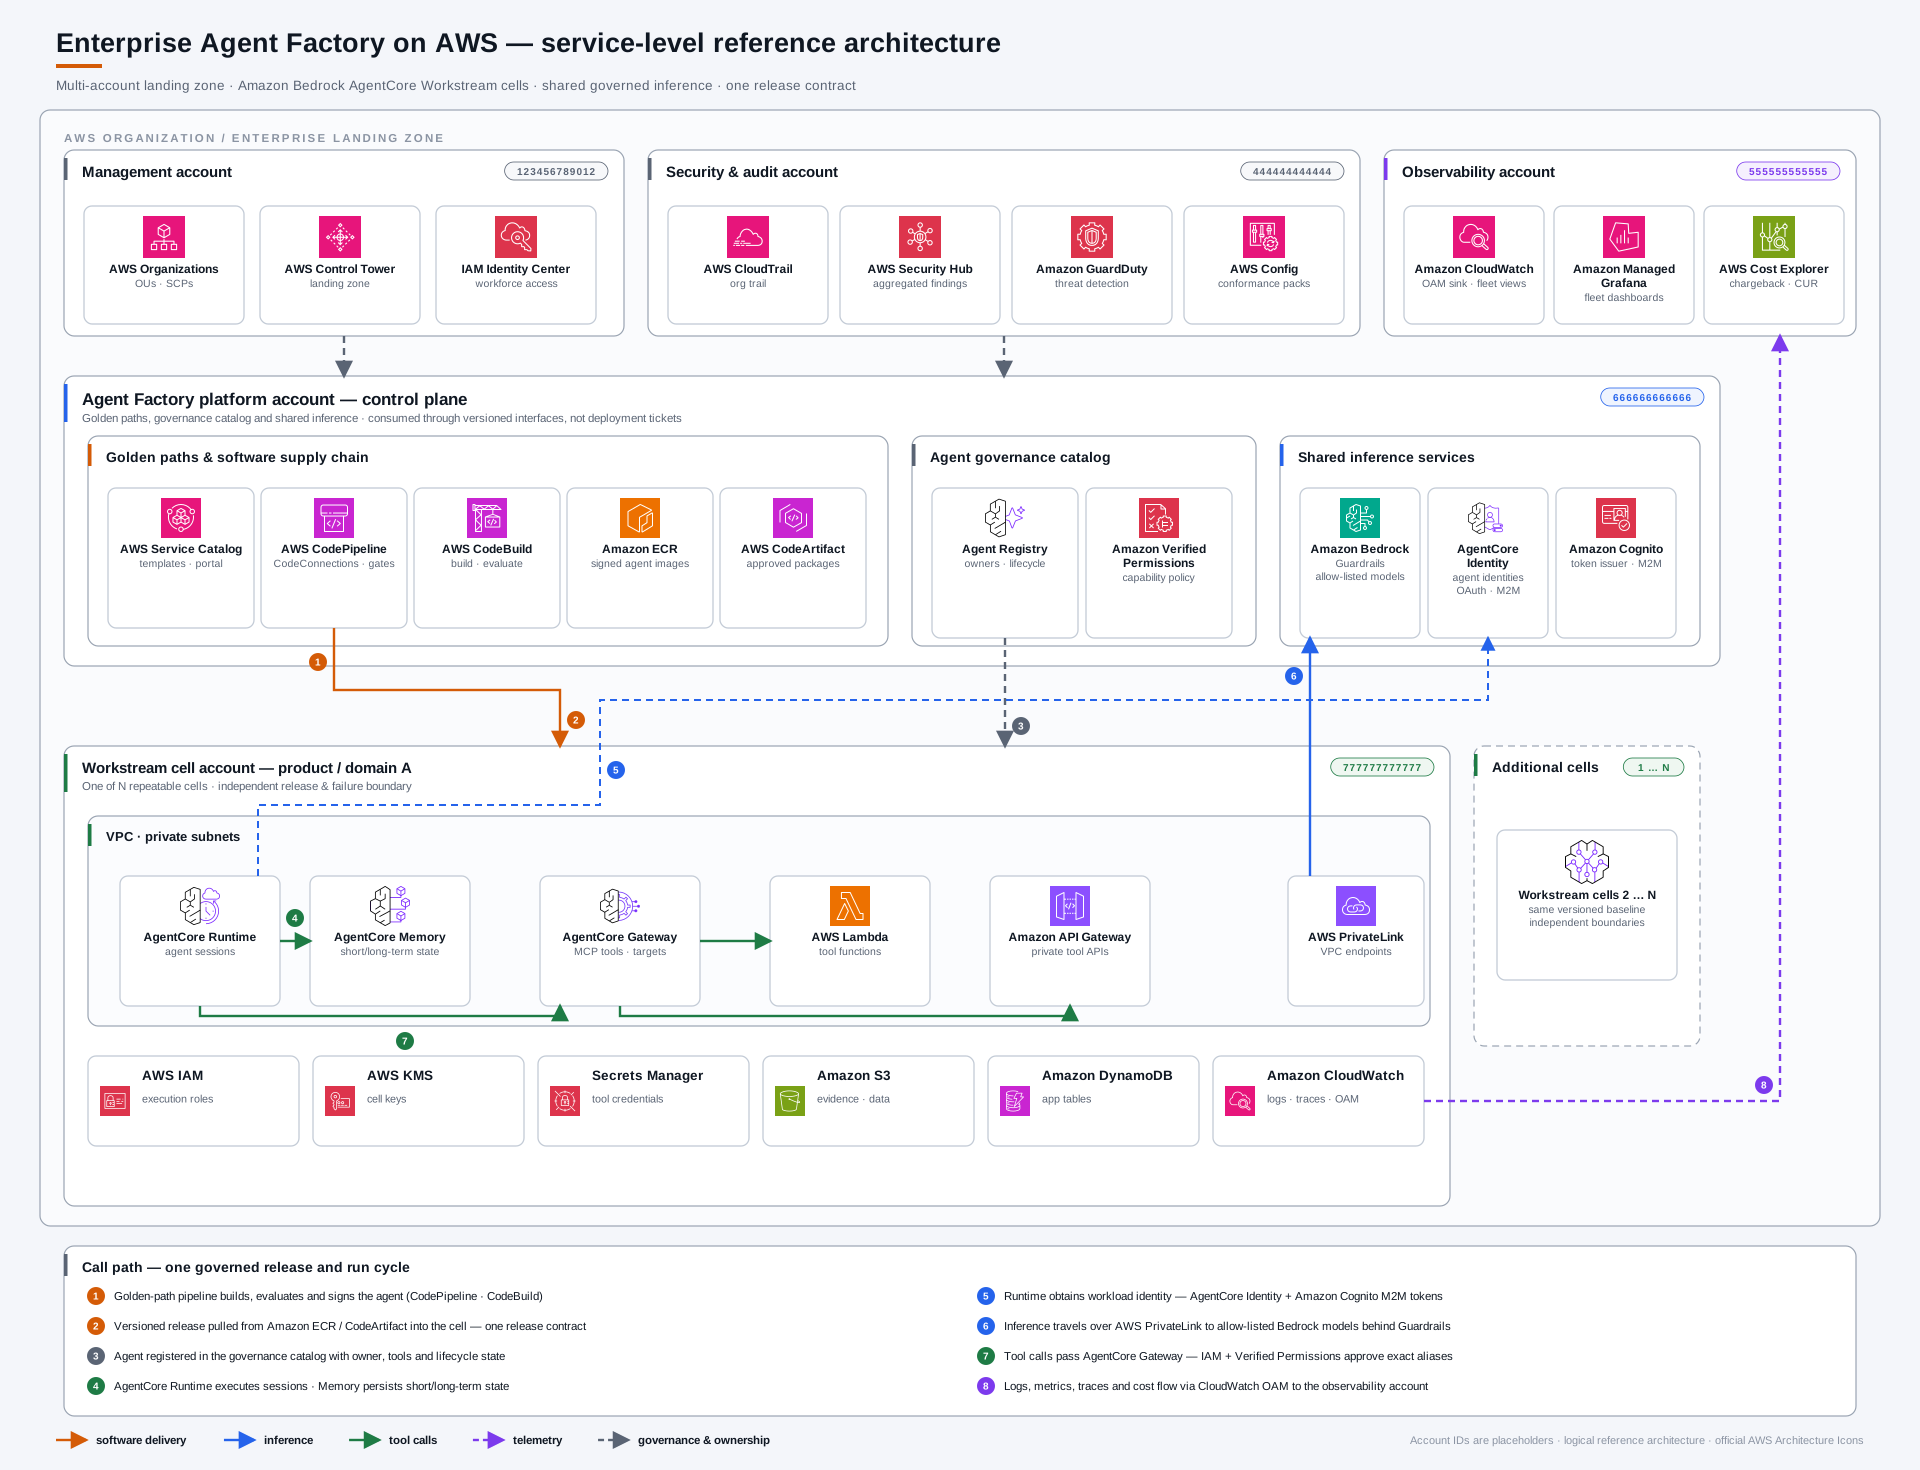
Known limitations and support envelope
Each item is copied from the project README or docs without paraphrase.
- Any substituted LLM Gateway, Tool Gateway, runtime, memory, identity, registry, policy, delivery, observability, or safety implementation until its full contract matrix passes. README.md: Outside the current envelope (opens in new tab)
- A demonstrated rollout to hundreds of engineers or a measured fleet-capacity benchmark. README.md: Outside the current envelope (opens in new tab)
- Any Region other than
eu-west-1until independently validated. README.md: Outside the current envelope (opens in new tab) - Legacy direct-Bedrock evaluation, online-evaluation, ECS LiteLLM, and direct circuit-breaker paths that rely on cross-Region profiles. README.md: Outside the current envelope (opens in new tab)
- VPC Lattice private endpoints. README.md: Outside the current envelope (opens in new tab)
- Transaction Search enabled by default. README.md: Outside the current envelope (opens in new tab)
- Native Gateway rate limiting as a hard quota or authorization control. README.md: Outside the current envelope (opens in new tab)
- Automatic retirement of the Lambda Cedar wrapper. README.md: Outside the current envelope (opens in new tab)
- A compliance certification, availability SLA, or guarantee that future AWS changes preserve behavior. README.md: Outside the current envelope (opens in new tab)
- Runtime network posture. Network posture:
networkMode = PUBLIC, matching the live commit. d03-workstream-runtime-memory-stack.ts (opens in new tab) - Evaluation gate. This is a scaffolded implementation evaluation_gate.py (opens in new tab)
- Region support. A Region is supportable only after independent service-availability, model and residency, IAM/SCP, availability-zone, strict synth, positive/adversarial, rollback, observability, and teardown gates pass there. Do not extrapolate from Ireland. README.md: Outside the current envelope (opens in new tab)
Evidence
The README defines local gates, a strict synth for infrastructure changes, and seven conditions that a behavior-changing revision must meet before it counts as complete.
What runs against live AWS
Live mode fails closed: missing credentials, probes, resources, or expected denials are errors, not passing skips. The adversarial harness validates the evidence schema, twin ledger, sanitization, and domain catalog offline.
Source: enterprise-agentic-ai-platform-blueprint/README.md: 6.6 Validation (opens in new tab), enterprise-agentic-ai-platform-blueprint/README.md: 10.2 Threat and evidence model (opens in new tab)
Live-validated reference envelope
Each item is copied from the README without paraphrase and links its source.
- Platform and Workload pipelines through production. README.md: Live-validated reference envelope (opens in new tab)
- AWS Agent Registry record resolution and governance. README.md: Live-validated reference envelope (opens in new tab)
- Generated agents using LiteLLMModel and MCPClient. README.md: Live-validated reference envelope (opens in new tab)
- AgentCore Identity, Runtime, Memory, Inference Gateway, and Tool Gateway. README.md: Live-validated reference envelope (opens in new tab)
- Benign and adversarial Guardrail calls with exact admitted and blocked outcomes. README.md: Live-validated reference envelope (opens in new tab)
- Exact HTTP 429 behavior for an unallocated model. README.md: Live-validated reference envelope (opens in new tab)
- Direct cross-account Runtime denial. README.md: Live-validated reference envelope (opens in new tab)
- Runtime update cancellation, rollback, and re-run while sampled sessions remained available. README.md: Live-validated reference envelope (opens in new tab)
- Evaluation gates for regression, quality, tool success, refusal, latency, and cost. README.md: Live-validated reference envelope (opens in new tab)
- Management queries across linked Platform and Workstream logs and metrics. README.md: Live-validated reference envelope (opens in new tab)
- Gateway application-log and OTEL span correlation after regional propagation. README.md: Live-validated reference envelope (opens in new tab)
- Dependency-ordered teardown and direct zero-residual inventories across all three account roles. README.md: Live-validated reference envelope (opens in new tab)
Local gates
npm run build
npm test
npm run lint
npm run scrub

python3 -m pytest tests/adversarial/unit -q
python3 -m pytest scripts/test_final_teardown.py scripts/test_residue_inventory.py -q
What a pass proves: The packages build, their unit tests and lint pass, the scrub script passes, the adversarial harness unit tests pass, and the teardown and residue-inventory scripts are tested.
Strict synth and cdk-nag for infrastructure changes
npx cdk synth --strictWhat a pass proves: The exact account and Region topology synthesizes, the generated templates are reviewed, and cdk-nag reports are clean.
Seven conditions for a behavior-changing revision
What a pass proves: A behavior-changing revision is complete only after all seven:
- reviewed pipeline deployment;
- an authorized positive call;
- an unauthorized adversarial twin with an exact denial;
- a mutation proving the test fails when the control is removed;
- rollback and re-run to green;
- centralized logs, metrics, and traces where claimed;
- dependency-ordered teardown and direct resource inventory.
Documentation on this site
- README: Enterprise Agentic AI Platform Blueprint on AWS
Teardown
Prerequisites and deployment sequence
Retire Platform alias grants first, then run the fail-closed teardown per account role: Workstream, then Platform, then Management. Each run is a dry run until you add --apply. Finish with the residue inventory.
python3 scripts/final_teardown.py \
  --account-role workstream \
  --expected-account <WORKSTREAM_ACCOUNT> \
  --region eu-west-1